Shadow AI Governance: Managing Unsanctioned AI in Enterprises
Shadow AI governance is the framework enterprises use to identify,...
Make email marketing simplified

Make email marketing simplified

Make email marketing simplified

Make email marketing simplified

Make email marketing simplified

Make email marketing simplified

Make email marketing simplified

Make email marketing simplified

Make email marketing simplified

Make email marketing simplified

Make email marketing simplified

Make email marketing simplified

Make email marketing simplified

Make email marketing simplified

Make email marketing simplified

We use cookies for our website to give you the most relevant experience by remembering your preferences. By clicking “accept”, you consent to use of ALL the cookies
This website uses cookies to improve your experience while you navigate through the website. Out of these, the cookies that are categorized as necessary are stored on your browser as they are essential for the working of basic functionalities of the website. We also use third-party cookies that help us analyze and understand how you use this website. These cookies will be stored in your browser only with your consent. You also have the option to opt-out of these cookies. But opting out of some of these cookies may affect your browsing experience.
Necessary cookies are absolutely essential for the website to function properly. These cookies ensure basic functionalities and security features of the website, anonymously.
| Cookie | Duration | Description |
|---|---|---|
| cookielawinfo-checkbox-functional | 11 months | This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category “Analytics”. |
| cookielawinfo-checkbox-functional | 11 months | The cookie is set by GDPR cookie consent to record the user consent for the cookies in the category “Functional”. |
| cookielawinfo-checkbox-necessary | 11 months | This cookie is set by GDPR Cookie Consent plugin. The cookies is used to store the user consent for the cookies in the category “Necessary”. |
| cookielawinfo-checkbox-others | 11 months | This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category “Other. |
| cookielawinfo-checkbox-performance | 11 months | This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category “Performance”. |
| viewed_cookie_policy | 11 months | The cookie is set by the GDPR Cookie Consent plugin and is used to store whether or not user has consented to the use of cookies. It does not store any personal data. |
Functional cookies help to perform certain functionalities like sharing the content of the website on social media platforms, collect feedbacks, and other third-party features.
Performance cookies are used to understand and analyze the key performance indexes of the website which helps in delivering a better user experience for the visitors.
Analytical cookies are used to understand how visitors interact with the website. These cookies help provide information on metrics the number of visitors, bounce rate, traffic source, etc.
Advertisement cookies are used to provide visitors with relevant ads and marketing campaigns. These cookies track visitors across websites and collect information to provide customized ads.
Other uncategorized cookies are those that are being analyzed and have not been classified into a category as yet.
Cyberia Tech, Inc. respects your privacy. This Privacy Policy explains how we collect, use, and share your information. By using our services, you agree to this policy. If any other agreements conflict with this Privacy Policy, the terms of those agreements prevail.
Cyberia Tech complies with the EU-US and Swiss-US Privacy Shield Frameworks for handling personal data from the EEA, UK, and Switzerland. In case of any conflict, the Privacy Shield Principles prevail. Learn more at Privacy Shield. Key Definitions
Information linked to an individual, transferred from the EEA, UK, or Switzerland to the U.S.
Data revealing race, religion, health, sexual orientation, and similar categories.
Effective Date: [ 2026 / 11 / 11 ]
Welcome to The Cyberia Tech ! By accessing or using our website or services, you agree to
comply with and be bound by these Terms of Use and our Privacy Policy. If you do not agree with
these terms, please do not use our Services.
Loading
0 %
Your First Piece of the Puzzle in
Business Growth


Shadow AI governance is the framework enterprises use to identify, manage, and secure employee use of unsanctioned generative AI tools. Rather than attempting to block all AI access at the network level, effective governance provides secure, monitored internal gateways that prevent sensitive corporate data from training public language models while maintaining employee productivity.
When an operations manager needs to summarize a 50-page vendor contract, they will rarely wait for an officially sanctioned procurement tool. They will simply paste the sensitive document into a free, public browser-based language model. The Slack Workforce Lab found in its March 2024 survey that 60% of employees using artificial intelligence at work currently operate without formal guidance or training. This disconnect creates a massive security blind spot for IT leaders. The decision facing organizations is no longer whether your enterprise will adopt generative AI, but whether you will manage it proactively or eventually discover your intellectual property in a public model’s training data.
Employees turn to unsanctioned artificial intelligence because consumer-facing tools remove operational friction. They offer immediate utility for tasks ranging from drafting marketing copy to writing boilerplate Python scripts. The severe risk emerges from the data pipelines powering these consumer tiers. When a user interacts with a free, web-based large language model (LLM), the provider’s terms of service typically allow the platform to ingest prompt data to refine and train future iterations of their base models.
This ingestion mechanism directly compromises corporate data confidentiality. If an engineer pastes proprietary source code into a public chat interface to find a bug, that code becomes part of the platform’s dataset. According to Gartner’s recent projections, 80% of enterprises will have deployed generative AI by 2026, a massive shift from just 5% early in 2023. However, this statistic primarily tracks official, sanctioned deployments. The unofficial usage rate—happening on personal accounts via corporate laptops—is significantly higher.
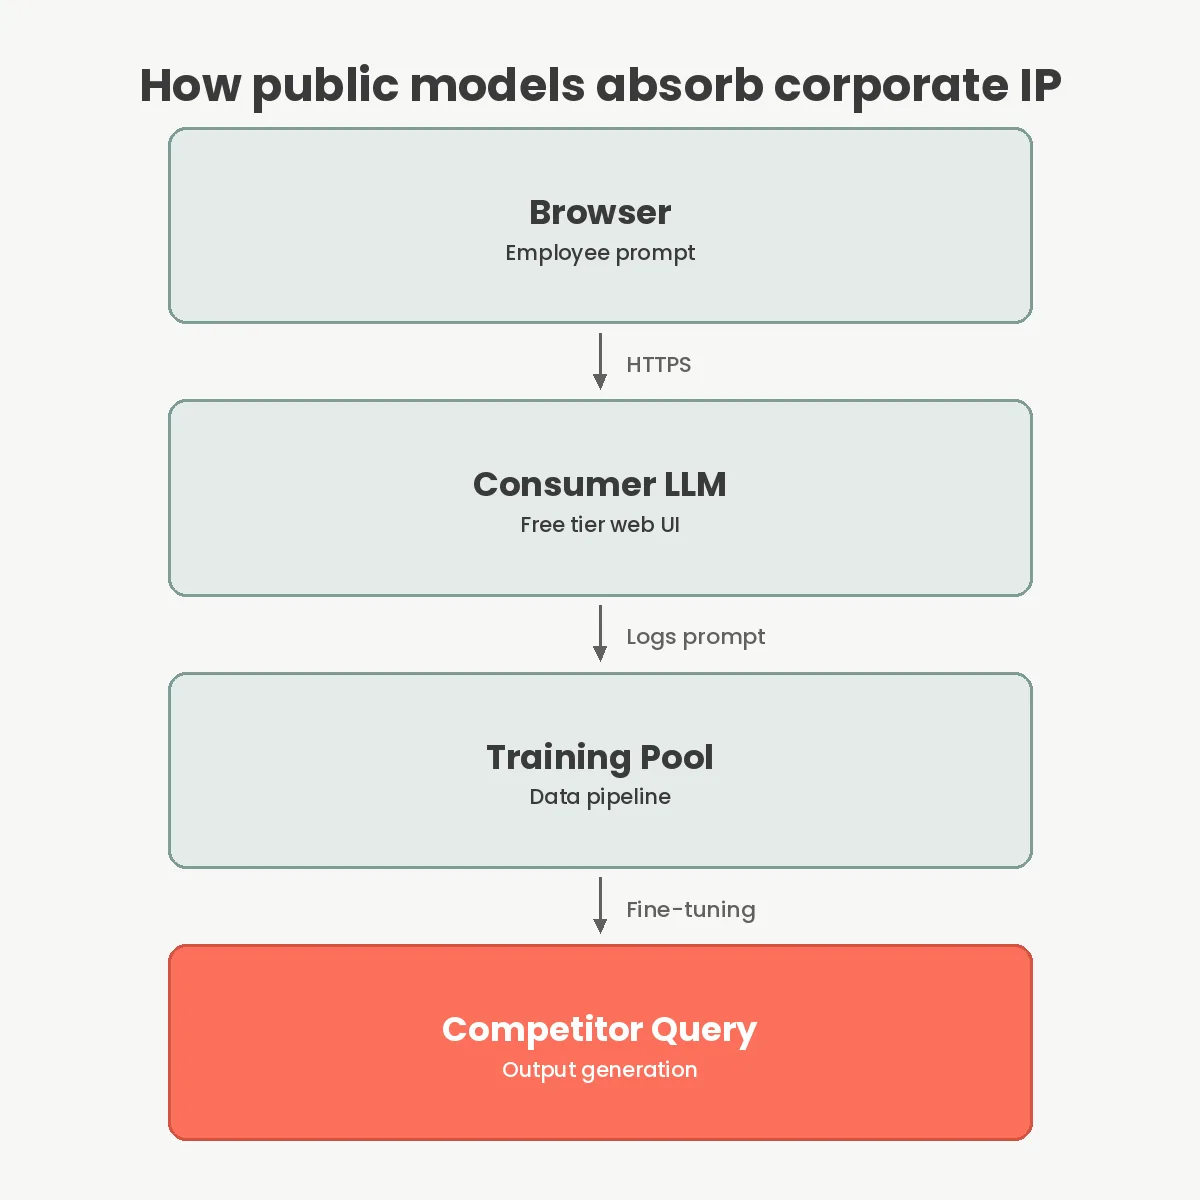
When IT procurement cycles take six to nine months to vet and approve a new enterprise software vendor, the gap between employee needs and provided tools widens. Workers optimizing for speed will always bypass sluggish processes. They utilize browser extensions, unauthorized mobile applications, and web interfaces that operate entirely outside of corporate logging and monitoring infrastructure.
Faced with uncontrolled data flow, network administrators often default to restrictive measures. They update secure web gateways and DNS filters to block access to known AI domains. This approach immediately creates a tactical arms race that the IT department cannot win.
While blocking a handful of high-profile domains is trivial, the generative AI ecosystem expands daily. Hundreds of new wrapper applications—platforms built directly on top of commercial APIs—launch every week. An IT team cannot maintain an exhaustive blocklist of every unvetted AI startup on the internet. Furthermore, determined employees simply switch to personal devices or cellular networks to complete their work, completely blinding the organization to the data movement.
| Enforcement Method | Implementation Time | Effectiveness | Employee Friction |
|---|---|---|---|
| DNS / Domain Blocking | Hours | Low (circumvented easily) | High |
| Acceptable Use Policy | Days | Very Low | None |
| Internal API Gateway | Weeks | High (secures data) | Low |
| Endpoint DLP Agents | Months | Medium | High |
Instead of securing the perimeter, aggressive blocking incentivizes users to hide their activity. When organizations enforce strict network bans without providing viable alternatives, they lose the ability to measure which departments actually require AI augmentation. This prevents strategic investment and leaves leadership entirely in the dark regarding actual operational workflows.
The consequences of unsanctioned generative AI usage are severe enough that Cisco’s 2024 Data Privacy Benchmark reported 27% of enterprises temporarily banned these tools entirely. They enacted these bans specifically due to privacy concerns and the fear of irretrievable data leakage.
The Open Worldwide Application Security Project (OWASP) classifies this specific threat vector under its Top 10 for LLM Applications as LLM06: Sensitive Information Disclosure. When users interact with models without boundary controls, they inadvertently expose intellectual property, financial projections, and personally identifiable information (PII). Because neural networks do not store data in traditional databases, you cannot simply query and delete a leaked document. Once proprietary information influences the model’s weights during a fine-tuning run, extracting it is nearly impossible.
This reality severely impacts regulatory compliance. Organizations operating under GDPR, HIPAA, or SOC2 frameworks face massive liabilities if an employee uses consumer AI to summarize patient records or user telemetry. The fines associated with these breaches far exceed the cost of implementing proper shadow AI governance.
One of the most common mistakes enterprises make is assuming a legal document constitutes a technical solution. Organizations frequently update their acceptable use policy (AUP), send an annual compliance email stating that company data must not enter public models, and consider the governance problem solved. This is the policy-only trap.
A static policy document does not alter human behavior when an unsanctioned tool saves an employee three hours of tedious formatting work every single day. Users mentally justify the violation because they view the productivity gain as beneficial to the company. When policies directly conflict with operational efficiency, the policy always loses.
Another prevalent failure mode involves relying solely on endpoint data loss prevention (DLP) scanners. Legacy DLP software struggles to identify contextual IP leaks within conversational prompts. An employee asking an AI to “analyze these quarterly revenue projections” might not trigger a traditional regex filter looking for credit card numbers, but it still constitutes a critical data leak.
To eliminate shadow AI, an enterprise must provide a sanctioned alternative that matches or exceeds the convenience of public consumer tiers. The most effective architectural approach is deploying an internal corporate AI gateway. This internal portal acts as a managed proxy between the workforce and commercial language models.
When an employee accesses the internal gateway, they authenticate via the company’s existing identity provider. The gateway then routes their prompts through an API layer. The critical distinction here is the licensing agreement. When enterprises purchase API access from major cloud providers—rather than using consumer web interfaces—the contracts explicitly guarantee that prompt data and generated responses are not retained or used for model training.
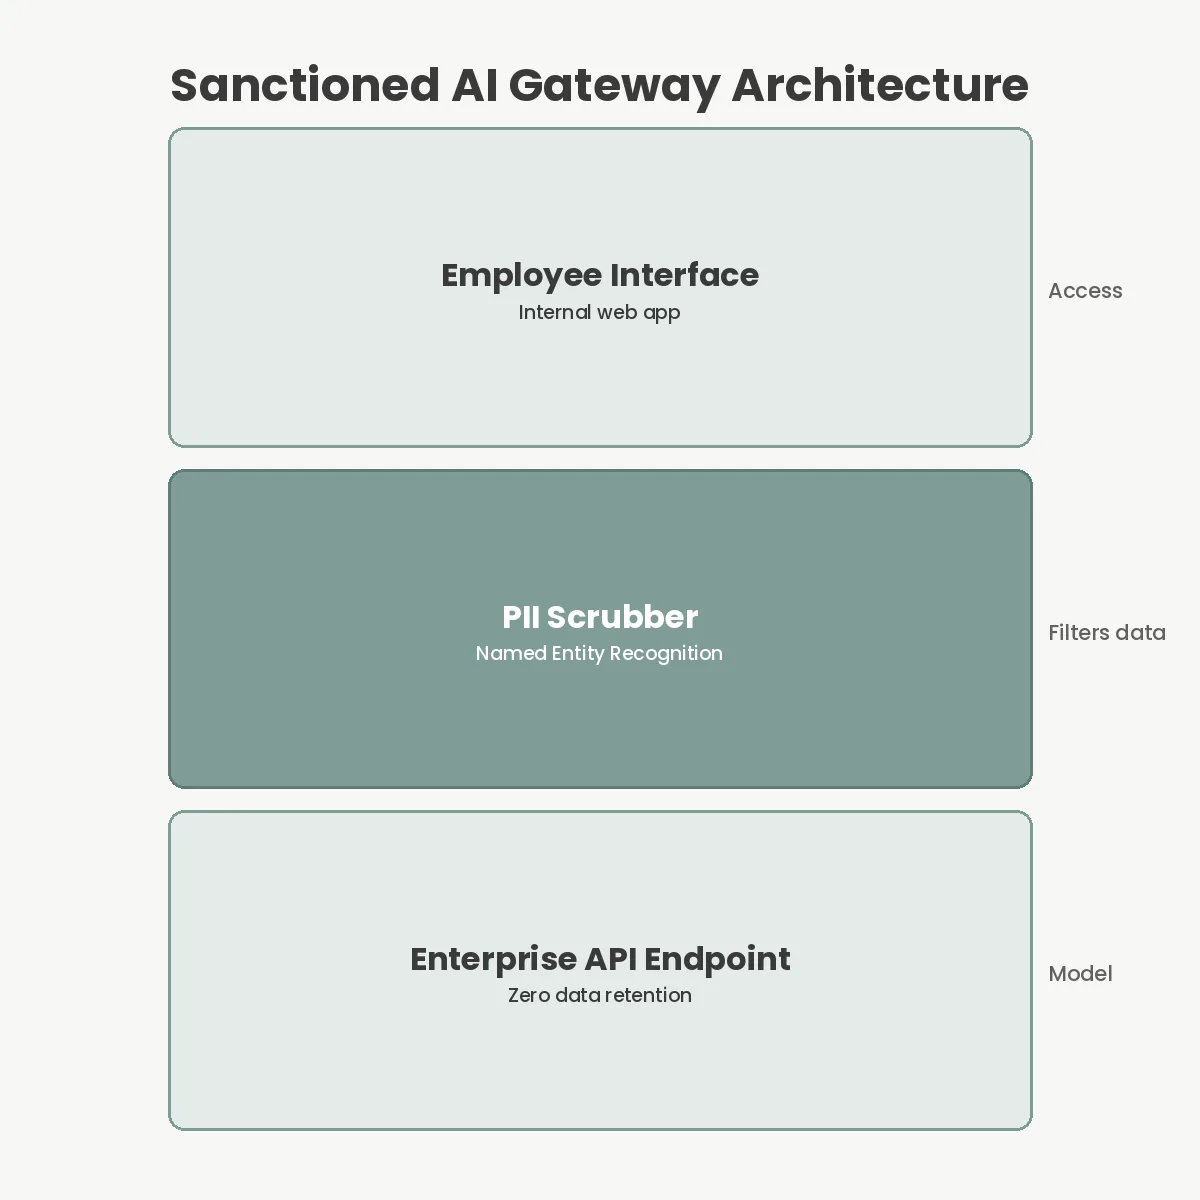
Advanced organizations build additional security directly into this layer. Before a prompt ever leaves the corporate network, the gateway can run local scrubbing algorithms—often powered by small, specialized models—to strip out PII, API keys, or financial markers. By integrating this setup with modern zero trust network access architecture, IT can meticulously log which departments utilize specific models, calculate exact token usage, and enforce granular access controls without slowing down the end user.
Providing official, governed access carries hard operational costs. Enterprise-grade licenses for platforms like Microsoft Copilot or ChatGPT Enterprise typically require investments around $30 per user per month. For an organization of 5,000 employees, rolling out ubiquitous access represents a $1.8 million annual commitment. This financial reality often causes hesitation at the executive level.
However, forcing engineering and operations teams to work without these tools is functionally equivalent to denying them cloud infrastructure. To justify the budget, technology leaders must calculate the concrete return on investment. If enterprise AI coding assistants save a developer two hours a week, the $30 monthly license pays for itself within the first three days of the month.
Furthermore, organizations can fund these initiatives by consolidating enterprise SaaS vendors. Auditing existing software stacks frequently reveals redundant licenses and legacy tools that can be retired to reallocate budget toward secure, governed generative AI gateways.
Shadow AI includes any unsanctioned generative AI tool, language model, or browser extension employees use for work tasks without explicit IT approval. Because these tools lack corporate oversight, they introduce significant data privacy and security vulnerabilities.
Network firewalls struggle to block shadow AI because new models, wrapper applications, and web interfaces launch daily. Maintaining an exhaustive blocklist is labor-intensive, and employees can easily bypass restrictions using personal devices or cellular networks.
An internal AI gateway proxy sits between employees and the language model, authenticating users and utilizing enterprise API endpoints. These specific commercial API contracts legally guarantee that prompt data is never retained for future model training.
Written acceptable use policies fail because they conflict directly with operational efficiency. When an unsanctioned tool saves an employee hours of tedious work, they will consistently prioritize personal productivity over static compliance documents.
Securing enterprise intellectual property in the age of generative models requires structural shifts, not just longer blocklists. Shadow AI governance succeeds only when the IT organization transitions from a posture of denial to one of secure provision. By deploying an internal AI gateway backed by commercial APIs with zero-retention guarantees, businesses mitigate the severe risk of data exposure. Your immediate next action is to audit network logs for unmanaged API traffic, quantify the real demand for language models across your departments, and secure the budget required to license secure enterprise endpoints.
You Can Get More Information!